Recent Posts
31
Information / Re: PHP Foundation: Critical PHP Security Releases (8.5.12, 8.4.27, 8.3.36, 8.2.35)
« Last post by Martins-phpbb on October 24, 2026, 01:25:49 PM »32
PHP / Re: CWP system PHP 8.3.36 UPDATE (CVE)
« Last post by 6Sense on October 24, 2026, 12:53:31 PM »I'm confused.
On Alma 8.1 & CWP 1.23 (PHP FPM all updated to patched version). The CWP services however are still running on the existing PHP 7.2 runtime.
I can see the new update script, I imagine it is supposed to install the 8.3 update (/scripts/update_cwpphp83). This script though doesn't seem to be called by the cron when I run /scripts/update_cwp, twice or otherwise. I haven't run it directly as not sure what it will do.
/usr/local/cwp/.conf/.cwpphp83.done does not exist.
I'm thinking the bones are there but for me the update is not being tiggered.
33
PHP / Re: CWP system PHP 8.3.36 UPDATE (CVE)
« Last post by darianrizaludin on October 24, 2026, 11:26:28 AM »Dear all, has this issue been resolved? I would like to proceed with the upgrade, but I am concerned about encountering an error.
34
PHP / Re: Update your PHP ASAP 🚨
« Last post by muscator on October 24, 2026, 11:23:42 AM »On almalinux9, running the new php-fpm 8.3.36 and cwppro 1.23 - the internal cwp php version is still:
/usr/local/cwp/php71/bin/php -v
PHP 7.4.33 (cli) (built: Apr 26 2023 00:00:00) ( NTS )
Copyright (c) The PHP Group
Zend Engine v3.4.0, Copyright (c) Zend Technologies
with the ionCube PHP Loader + ionCube24 v15.5.0, Copyright (c) 2002-2026, by ionCube Ltd.
Apparently others run the internal 8.3.36 and not the old 7.4.33
Any suggestions why?
35
Information / Re: Possible CWP Security Issue – Malicious JavaScript Injection
« Last post by Freespirits_GR_Host on October 24, 2026, 08:51:16 AM »Thanks for sharing this finding. Checking the temporary directories of individual hosting accounts is definitely worthwhile during a compromise investigation.
However, I would be careful with the cleanup script. Deleting everything under /home/*/tmp can remove legitimate PHP sessions, application-generated files and potentially valuable forensic evidence.
Before deleting anything, I would first inventory the PHP files:
find /home -type f -path '*/tmp/*.php' \
-printf '%TY-%Tm-%Td %TH:%TM %u %p\n'
Then examine suspicious files individually without executing them:
stat /path/to/suspicious.php
sha256sum /path/to/suspicious.php
file /path/to/suspicious.php
I would also check whether these files contain suspicious encoded payloads, unexpected command-execution functions or references to unfamiliar external servers.
Most importantly, correlate their creation times with website access logs. If the same suspicious PHP payload appears under multiple hosting accounts, investigate whether a shared vulnerability or server-level persistence mechanism is responsible.
Preserve suspicious samples before removing them. If root compromise is suspected, consider isolating the server and recovering from a trusted installation.
Full disclosure: I'm the developer of the CWP7 Security Audit Module. I developed it to help CWP administrators investigate suspicious files and persistence indicators. It may help with a broader server-wide investigation, although its coverage of these particular temporary directories should be verified.
Have you checked whether the suspicious files share identical hashes or reappear after deletion? That could help determine whether you're dealing with repeated application infections or an active persistence mechanism.
36
PHP / Re: CWP system PHP 8.3.36 UPDATE (CVE)
« Last post by djprmf on October 24, 2026, 08:14:45 AM »I can also confirm the bug with the email listing.
Is giving the same error in every server CWP that i have updated.
Is giving the same error in every server CWP that i have updated.
37
Information / Re: PHP Foundation: Critical PHP Security Releases (8.5.12, 8.4.27, 8.3.36, 8.2.35)
« Last post by Painkiller88 on October 24, 2026, 08:11:57 AM »There is still another thing i don't get.
Why is the CWP internal PHP still using 7.2.30, is there any way to update this and why isn't this update not comming from the devs itself?
And there is no newer version available:
[root@srv1 ~]# dnf --refresh --showduplicates list cwpphp
CentOS Web Panel repo for Linux 8 - x86_64 20 kB/s | 2.9 kB 00:00
AlmaLinux 8 - BaseOS 7.1 kB/s | 3.8 kB 00:00
AlmaLinux 8 - AppStream 8.7 kB/s | 4.3 kB 00:00
AlmaLinux 8 - Extras 6.5 kB/s | 3.3 kB 00:00
AlmaLinux 8 - PowerTools 8.5 kB/s | 4.2 kB 00:00
AlmaLinux 8 - PowerTools Source 6.0 kB/s | 3.0 kB 00:00
AlmaLinux 8 - PowerTools debuginfo 5.9 kB/s | 3.0 kB 00:00
Extra Packages for Enterprise Linux 8 - x86_64 62 kB/s | 36 kB 00:00
MariaDB 4.5 kB/s | 3.0 kB 00:00
nginx repo 25 kB/s | 3.0 kB 00:00
varnishcache_varnish64 324 B/s | 833 B 00:02
varnishcache_varnish64-source 343 B/s | 833 B 00:02
Veeam Backup for GNU/Linux - x86_64 12 kB/s | 3.0 kB 00:00
Installed Packages
cwpphp.x86_64 7.2.30-3 @cwp
Available Packages
cwpphp.x86_64 7.0.14-3 cwp
cwpphp.x86_64 7.0.15-1 cwp
cwpphp.x86_64 7.0.15-2 cwp
cwpphp.x86_64 7.0.16-1 cwp
cwpphp.x86_64 7.0.16-2 cwp
cwpphp.x86_64 7.0.16-4 cwp
cwpphp.x86_64 7.0.17-1 cwp
cwpphp.x86_64 7.0.24-1 cwp
cwpphp.x86_64 7.0.24-2 cwp
cwpphp.x86_64 7.0.32-1 cwp
cwpphp.x86_64 7.2.30-1 cwp
cwpphp.x86_64 7.2.30-3 cwp
[root@srv1 ~]#
38
PHP / Re: Update your PHP ASAP 🚨
« Last post by djprmf on October 24, 2026, 08:11:13 AM »Updating to the latest version leads to a PHP error with the PCRE module, like @emerysteele stated.
The commands provided solved the issue! Thanks emerysteele!
And indeed:
The commands provided solved the issue! Thanks emerysteele!
And indeed:
Code: [Select]
/usr/local/cwp/php71/bin/php -v
PHP 8.3.36 (cli) (built: Oct 22 2026 14:30:10) (NTS)
Copyright (c) The PHP Group
Zend Engine v4.3.36, Copyright (c) Zend Technologies
    with the ionCube PHP Loader v15.5.1, Copyright (c) 2002-2026, by ionCube Ltd.
39
PHP / Re: CWP system PHP 8.3.36 UPDATE (CVE)
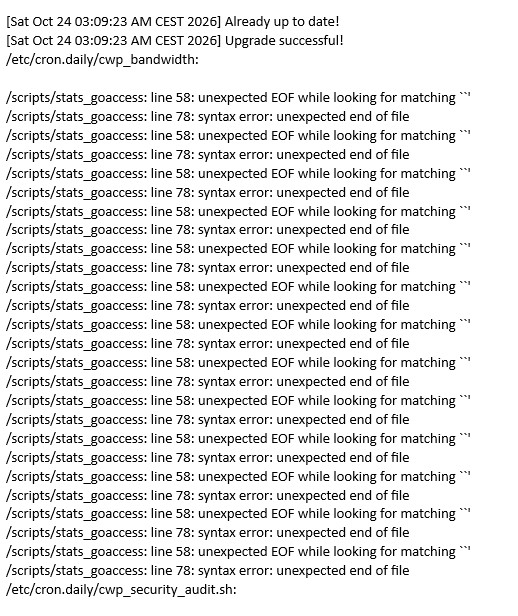
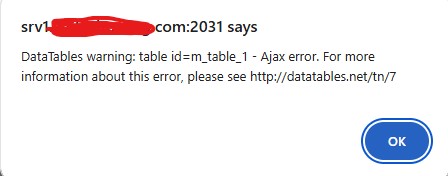
« Last post by zakrpa on October 24, 2026, 07:10:19 AM »See this in email stats goaccess last 2 days, and can confirm this email list problem too.
40
PHP / Re: Update your PHP ASAP 🚨
« Last post by emerysteele on October 24, 2026, 04:48:51 AM »Looks like my machine for whatever reason was trying to use an older pcre module, even though it has newer one too?
Did this to fix it:
Can undo with this if dont fix:
Did this to fix it:
Code: [Select]
mkdir -p /root/pcre2_local_backup
mv /usr/local/lib/libpcre2* /root/pcre2_local_backup/
ldconfig
systemctl restart cwpsrv-phpfpm
systemctl restart cwp-phpfpm
systemctl restart cwpsrv
systemctl restart httpd
/scripts/update_cwp
Can undo with this if dont fix:
Code: [Select]
mv /root/pcre2_local_backup/* /usr/local/lib/ && ldconfig