New in CWP Edge-LatestFree with every CWPpro licenceWebsites up to 300x faster
Get CWPpro ›
CWP now includes LSPHP, LSAPI-Cache and CWP Cage at no extra cost with all CWPpro licences. The LSAPI-Cache plugin is integrated into our WordPress and other script installers, and CWP Cage gives every user complete isolation. Available now in the CWP Edge-Latest version.
Recent posts
#21
Updates / CWP New Version Released 2.0.5...
Last post by Administrator - November 14, 2026, 10:26:33 PMCWP 2.0.5 (edge) – changes since 2.0.4
Fixes
- User-panel login: fixed sign-in failing right after a logout, and on servers where the PHP
session does not persist. Logging out destroyed the session that held the freshly rendered
login CSRF token, so the next sign-in was rejected with "failed". The token is now also
carried in a short-lived HttpOnly cookie (double-submit), so it survives a destroyed or
non-persistent session while still blocking login CSRF. The login page also returns a proper
error instead of a blank page when a request is refused. (#504017)
- Update reliability: an update interrupted part-way (for example a package-manager or mirror
error mid-run, as seen on CentOS 7 after the SCLo repositories moved to vault) no longer
leaves the panel stuck half-updated with a newer version number than its actual code. The
updater now records the code version it actually applied and, if the stored version is ahead
of it, re-applies the panel code on the next run instead of skipping it.
- Dashboard: fixed a false "MariaDB is stopped" warning (and the matching health-score dip) on
servers where the database runs under a different service name (mysqld/mysql) or outside
systemd; the dashboard now treats its own live database connection as the source of truth and
only falls back to the service check.
- Nginx (php-fpm mode): the "Block malicious requests" HTTPS vhost template was a copy of the
reverse-proxy template, so an unresolved proxy placeholder disabled the SSL vhost and HTTPS
fell back to the self-signed certificate. It is now a proper php-fpm (fastcgi) SSL template
that keeps the bad-robot and xmlrpc blocks. (#402220)
Fixes
- User-panel login: fixed sign-in failing right after a logout, and on servers where the PHP
session does not persist. Logging out destroyed the session that held the freshly rendered
login CSRF token, so the next sign-in was rejected with "failed". The token is now also
carried in a short-lived HttpOnly cookie (double-submit), so it survives a destroyed or
non-persistent session while still blocking login CSRF. The login page also returns a proper
error instead of a blank page when a request is refused. (#504017)
- Update reliability: an update interrupted part-way (for example a package-manager or mirror
error mid-run, as seen on CentOS 7 after the SCLo repositories moved to vault) no longer
leaves the panel stuck half-updated with a newer version number than its actual code. The
updater now records the code version it actually applied and, if the stored version is ahead
of it, re-applies the panel code on the next run instead of skipping it.
- Dashboard: fixed a false "MariaDB is stopped" warning (and the matching health-score dip) on
servers where the database runs under a different service name (mysqld/mysql) or outside
systemd; the dashboard now treats its own live database connection as the source of truth and
only falls back to the service check.
- Nginx (php-fpm mode): the "Block malicious requests" HTTPS vhost template was a copy of the
reverse-proxy template, so an unresolved proxy placeholder disabled the SSL vhost and HTTPS
fell back to the self-signed certificate. It is now a proper php-fpm (fastcgi) SSL template
that keeps the bad-robot and xmlrpc blocks. (#402220)
#22
Updates / CWP New Version Released 1.30...
Last post by Administrator - November 14, 2026, 10:25:37 PMCWP 1.30.13 (LTS) - changes since 1.30.10
Security
- Security Audit - credential-stealer detection. An unowned shared library (one no package owns) loaded into a
credential-handling daemon - SSH, the Dovecot/Postfix mail stack, OpenDKIM or saslauthd - is now reported as a
CRITICAL credential-stealer finding, and the alert lists every process that loads it (it previously named only the
one service being scanned, hiding that SSH and the mail daemons were the real carriers). This detection does not rely
on the standard package-verify check, which a tampered package db can make look clean. (#905352)
- Security Audit - the anti-rootkit library scan no longer looks broken. The dedicated scan needs a statically-linked
helper (a rootkit that tampers with the system libraries cannot fool a static tool). The audit no longer prints a
failure-looking line when none is present: it now also uses a system static helper when one is installed, and
otherwise prints a clear note that this optional scan was skipped (nothing was flagged, the general check still runs)
with how to enable it. (forum 15331)
- PHP Defender. The hardening rules no longer break a site that legitimately writes a debug log file (for example
WordPress debug logging is now allowed), while only the malicious case (a log sent to a script path) is still
blocked. The incidents viewer also reads the attacker address from the web-server log when the site runs behind the
nginx-to-Apache proxy. (#127406)
- ModSecurity manager (user panel) - hardening. Values built from a domain name are now fully quoted when used
(defense in depth; access was already restricted to the account's own domains).
- Statistics (user panel) - hardening. The domain and file names shown on the page are now safely escaped.
Fixes
- Admin menu language reliably follows your panel language (LANGADMIN). Two problems are fixed. First, one special
character in any value of the panel config file could make the whole file unreadable, so the admin language was lost
and the menu fell back to English; the language is now read directly. Second, the menu translations were looked up in
files that were not shipped in the LTS build, so every lookup fell back to English even when the translation existed -
those translation files (34 languages) are now shipped, and the menu follows your chosen language. (forum 15315)
- User panel speed. The panel rebuilt every page template from source on every request (about 280 KB of templates per
page), adding 100+ ms of pure compilation per page. Compiled templates are now cached per account (inside the
account's own home, isolated, refreshed when a template changes; it falls back safely if the cache cannot be
created). (#447329)
- Varnish cache purge. The user-panel purge could silently do nothing on servers with a non-standard Varnish admin
port or secret: the Varnish admin tool was called without the admin address and secret, and its auto-detect failed.
CWP now detects those from the running Varnish, then from the Varnish config, then from the standard default.
(#127406)
- WordPress Manager - db clone / staging. Cloning or staging a site could silently produce a near-empty db
(only the first table restored). The account's own limited db user could not replay the default db
export; the export is now taken with options that work with that limited user, so it restores completely. Also fixed:
the install registry could fail to write (a doubled config path) and the module could stop with a PHP error for any
account that already had a stored install. The WordPress command tool now runs with a per-request time limit, and
installing from a web address is restricted to the official WordPress.org source.
- Softaculous / Fantastico installs. Installs no longer fail with a MySQL-connection or invalid-token message: the
1.30.6 single-use local token broke installers that reuse one token across several API calls. The token is now
accepted for the length of its own short expiry instead of being used up on the first call, with the local-caller
restriction kept. (#787928)
- CWP-to-CWP Migration. The migration page no longer opens blank with an undefined-function error; the per-module
language helper is now present in the LTS code. (#841893)
- Nightly AutoSSL on a server with no domains. The nightly AutoSSL job no longer emails a missing-file error and a
related warning on a fresh server with no accounts or certificates yet. (forum 15314)
- Nightly no longer starts disabled PHP-FPM versions. The maintenance job added a monitor for every installed PHP-FPM
version and then started the ones switched off; it now monitors only versions that are enabled. (#460699)
- PHP extensions self-heal. The nightly job now decides per scan directory across all installed PHP versions, so a
shared settings file is no longer disabled because one command-line PHP cannot load a module that the account's web
PHP loads fine (which had broken WordPress with a 500). A genuinely missing module is still disabled. (#151688)
- Spam Annihilator. Removed a dead link in the user panel that opened a "module does not exist" page - Spam Annihilator
is a server-wide admin module and has no user-panel page. (forum 334369)
Improvements
- Apache Builder. Added Apache 2.4.71 to the version list (source on the CWP CDN). (forum 15326)
- ModSecurity rule set. The "OWASP latest" option is now labelled "OWASP CRS 3 (auto-updated to the latest 3.x
release)" so it is clear it tracks the OWASP CRS 3.x line (the option still auto-updates within 3.x). (forum 15328)
Security
- Security Audit - credential-stealer detection. An unowned shared library (one no package owns) loaded into a
credential-handling daemon - SSH, the Dovecot/Postfix mail stack, OpenDKIM or saslauthd - is now reported as a
CRITICAL credential-stealer finding, and the alert lists every process that loads it (it previously named only the
one service being scanned, hiding that SSH and the mail daemons were the real carriers). This detection does not rely
on the standard package-verify check, which a tampered package db can make look clean. (#905352)
- Security Audit - the anti-rootkit library scan no longer looks broken. The dedicated scan needs a statically-linked
helper (a rootkit that tampers with the system libraries cannot fool a static tool). The audit no longer prints a
failure-looking line when none is present: it now also uses a system static helper when one is installed, and
otherwise prints a clear note that this optional scan was skipped (nothing was flagged, the general check still runs)
with how to enable it. (forum 15331)
- PHP Defender. The hardening rules no longer break a site that legitimately writes a debug log file (for example
WordPress debug logging is now allowed), while only the malicious case (a log sent to a script path) is still
blocked. The incidents viewer also reads the attacker address from the web-server log when the site runs behind the
nginx-to-Apache proxy. (#127406)
- ModSecurity manager (user panel) - hardening. Values built from a domain name are now fully quoted when used
(defense in depth; access was already restricted to the account's own domains).
- Statistics (user panel) - hardening. The domain and file names shown on the page are now safely escaped.
Fixes
- Admin menu language reliably follows your panel language (LANGADMIN). Two problems are fixed. First, one special
character in any value of the panel config file could make the whole file unreadable, so the admin language was lost
and the menu fell back to English; the language is now read directly. Second, the menu translations were looked up in
files that were not shipped in the LTS build, so every lookup fell back to English even when the translation existed -
those translation files (34 languages) are now shipped, and the menu follows your chosen language. (forum 15315)
- User panel speed. The panel rebuilt every page template from source on every request (about 280 KB of templates per
page), adding 100+ ms of pure compilation per page. Compiled templates are now cached per account (inside the
account's own home, isolated, refreshed when a template changes; it falls back safely if the cache cannot be
created). (#447329)
- Varnish cache purge. The user-panel purge could silently do nothing on servers with a non-standard Varnish admin
port or secret: the Varnish admin tool was called without the admin address and secret, and its auto-detect failed.
CWP now detects those from the running Varnish, then from the Varnish config, then from the standard default.
(#127406)
- WordPress Manager - db clone / staging. Cloning or staging a site could silently produce a near-empty db
(only the first table restored). The account's own limited db user could not replay the default db
export; the export is now taken with options that work with that limited user, so it restores completely. Also fixed:
the install registry could fail to write (a doubled config path) and the module could stop with a PHP error for any
account that already had a stored install. The WordPress command tool now runs with a per-request time limit, and
installing from a web address is restricted to the official WordPress.org source.
- Softaculous / Fantastico installs. Installs no longer fail with a MySQL-connection or invalid-token message: the
1.30.6 single-use local token broke installers that reuse one token across several API calls. The token is now
accepted for the length of its own short expiry instead of being used up on the first call, with the local-caller
restriction kept. (#787928)
- CWP-to-CWP Migration. The migration page no longer opens blank with an undefined-function error; the per-module
language helper is now present in the LTS code. (#841893)
- Nightly AutoSSL on a server with no domains. The nightly AutoSSL job no longer emails a missing-file error and a
related warning on a fresh server with no accounts or certificates yet. (forum 15314)
- Nightly no longer starts disabled PHP-FPM versions. The maintenance job added a monitor for every installed PHP-FPM
version and then started the ones switched off; it now monitors only versions that are enabled. (#460699)
- PHP extensions self-heal. The nightly job now decides per scan directory across all installed PHP versions, so a
shared settings file is no longer disabled because one command-line PHP cannot load a module that the account's web
PHP loads fine (which had broken WordPress with a 500). A genuinely missing module is still disabled. (#151688)
- Spam Annihilator. Removed a dead link in the user panel that opened a "module does not exist" page - Spam Annihilator
is a server-wide admin module and has no user-panel page. (forum 334369)
Improvements
- Apache Builder. Added Apache 2.4.71 to the version list (source on the CWP CDN). (forum 15326)
- ModSecurity rule set. The "OWASP latest" option is now labelled "OWASP CRS 3 (auto-updated to the latest 3.x
release)" so it is clear it tracks the OWASP CRS 3.x line (the option still auto-updates within 3.x). (forum 15328)
#23
E-Mail / Roundcube Auto Login from CWP ...
Last post by ernlund - November 14, 2026, 09:40:54 PMHi,
I'm experiencing an issue with the automatic login to Roundcube when opening Webmail through the CWP User Panel.
The problem:
When I open Roundcube using the Webmail link in the CWP User Panel, the automatic login works initially. However, after approximately 1–2 minutes, Roundcube starts reporting IMAP authentication errors.
If I open Roundcube directly and log in manually using the mailbox email address and password, everything works correctly, even after remaining logged in for more than five minutes.
What I have investigated:
I have checked the Dovecot logs and found that:
The initial IMAP authentication through CWP Auto Login succeeds.
Subsequent IMAP authentication attempts also succeed initially.
After approximately two minutes, authentication starts failing.
The timing corresponds almost exactly to the expiration of the token used by CWP Auto Login.
I also checked the Dovecot SQL configuration and found that it uses the following logic:
IF(token_validity >= NOW(), token, password)
This means Dovecot accepts the temporary token only until its validity expires. After that, it falls back to the normal mailbox password.
The Roundcube session, however, appears to continue using the original temporary token after it has expired.
I have confirmed this by comparing the token validity timestamp in the postfix.mailbox database with the Dovecot authentication logs. The first failed login occurred just a few seconds after the token expired.
Environment:
Control panel: CentOS Web Panel (CWP)1.30.12
Roundcube: 1.6.21
Dovecot: MySQL authentication using the CWP mailbox database
IMAP host in Roundcube: localhost:143
My questions:
Has anyone else experienced IMAP authentication failures when using Roundcube through the CWP User Panel's automatic Webmail login?
Is the short validity period of the temporary Auto Login token intentional?
Is there a mechanism to renew or refresh the token while the Roundcube session is still active?
Is this a known issue, and is there a recommended fix?
Manual login directly through Roundcube works without any problems. The issue only occurs when using the automatic login from the CWP User Panel.
I would appreciate any feedback or suggestions.
Thanks!
I'm experiencing an issue with the automatic login to Roundcube when opening Webmail through the CWP User Panel.
The problem:
When I open Roundcube using the Webmail link in the CWP User Panel, the automatic login works initially. However, after approximately 1–2 minutes, Roundcube starts reporting IMAP authentication errors.
If I open Roundcube directly and log in manually using the mailbox email address and password, everything works correctly, even after remaining logged in for more than five minutes.
What I have investigated:
I have checked the Dovecot logs and found that:
The initial IMAP authentication through CWP Auto Login succeeds.
Subsequent IMAP authentication attempts also succeed initially.
After approximately two minutes, authentication starts failing.
The timing corresponds almost exactly to the expiration of the token used by CWP Auto Login.
I also checked the Dovecot SQL configuration and found that it uses the following logic:
IF(token_validity >= NOW(), token, password)
This means Dovecot accepts the temporary token only until its validity expires. After that, it falls back to the normal mailbox password.
The Roundcube session, however, appears to continue using the original temporary token after it has expired.
I have confirmed this by comparing the token validity timestamp in the postfix.mailbox database with the Dovecot authentication logs. The first failed login occurred just a few seconds after the token expired.
Environment:
Control panel: CentOS Web Panel (CWP)1.30.12
Roundcube: 1.6.21
Dovecot: MySQL authentication using the CWP mailbox database
IMAP host in Roundcube: localhost:143
My questions:
Has anyone else experienced IMAP authentication failures when using Roundcube through the CWP User Panel's automatic Webmail login?
Is the short validity period of the temporary Auto Login token intentional?
Is there a mechanism to renew or refresh the token while the Roundcube session is still active?
Is this a known issue, and is there a recommended fix?
Manual login directly through Roundcube works without any problems. The issue only occurs when using the automatic login from the CWP User Panel.
I would appreciate any feedback or suggestions.
Thanks!
#24
Information / Re: check all autoSSL (Lets en...
Last post by Netino - November 14, 2026, 08:21:36 PMQuote from: luca on November 13, 2026, 03:12:47 PMFrom devs via support
About the temporary URL (domain.com/~USERNAME or server-IP/~USERNAME): good idea. Showing that link for each account/domain in the panel would make previews before a DNS change easier. We've added it to the suggestions for our developers.
This is strongly discouraged for security reasons.
Once someone has your username, all they need is the password.
Worse still, there was a recent vulnerability in CWP where simply knowing the username was enough to execute commands that escalated privileges to root.
Therefore, you should not expose your username publicly, even during the initial testing phase. There are other alternatives for this—such as the `/etc/hosts` file on Linux, or `C:\Windows\System32\drivers\etc\hosts` on Windows—which allow you to point a domain to a specific IP address (in this case, your new IP).
Regards,
Netino
#25
SSL / AutoSSL with Cloudflare and re...
Last post by Wonder - November 14, 2026, 07:59:24 PMHello,
I'm running CWP 1.30.12 on AlmaLinux 10, using Cloudflare for DNS management and an external cloud firewall.
For security reasons, inbound HTTP/HTTPS traffic is restricted to Cloudflare's published IP ranges.
My DNS configuration is similar to this:
- `example.com` — Cloudflare proxied
- `www.example.com` — Cloudflare proxied
- `cpanel.example.com` — Cloudflare proxied
- `webmail.example.com` — Cloudflare proxied
- `mail.example.com` — DNS-only (not proxied, as required for mail services)
-The issue
When issuing a Let's Encrypt certificate through CWP AutoSSL, the main domain and proxied SANs are validated successfully, but validation fails when including `mail.example.com`.
Depending on the operation, CWP displays one of these messages:
- `None of SAN it is pointed.`
- `At this moment your domain can not be validated please try again in some minutes.`
I reproduced the same behavior on another server.
-Investigation and findings
I confirmed that CWP uses HTTP-01 validation through the following ACME configuration:
Since `mail.example.com` is DNS-only, Let's Encrypt must connect directly to the server to complete HTTP-01 validation. However, the external firewall restricts inbound TCP/80 to Cloudflare IP ranges.
As a test, I temporarily allowed inbound TCP/80 from all IPv4 and IPv6 sources, then:
The certificate was immediately issued successfully, including all SANs.
After issuance, I removed the temporary firewall rule.
This is expected HTTP-01 behavior rather than a certificate issuance bug in CWP.
-Questions
1. Does CWP AutoSSL support DNS-01 validation using the Cloudflare API, including the main domain and all SANs?
2. If DNS-01 is not currently supported, is there any plan to implement it?
3. Is there an officially supported method to use certificates issued and renewed independently through `acme.sh` (DNS-01), while preserving CWP's certificate installation, mail services integration and automatic renewals?
4. Is there an officially recommended or supported solution for automatically issuing and renewing SSL certificates in this scenario, without requiring unrestricted inbound HTTP access?
Ideally, I would like to continue using CWP's built-in AutoSSL functionality. However, I'm also open to managing certificates through `acme.sh` with DNS-01 validation, provided they can be reliably installed and used by CWP and its associated services, including mail, without conflicts during future updates.
Temporarily opening TCP/80 works as a manual workaround, but I'm looking for a reliable, fully automated solution that can be applied consistently across multiple CWP servers.
Any guidance or recommendations would be greatly appreciated.
Thank you!
I'm running CWP 1.30.12 on AlmaLinux 10, using Cloudflare for DNS management and an external cloud firewall.
For security reasons, inbound HTTP/HTTPS traffic is restricted to Cloudflare's published IP ranges.
My DNS configuration is similar to this:
- `example.com` — Cloudflare proxied
- `www.example.com` — Cloudflare proxied
- `cpanel.example.com` — Cloudflare proxied
- `webmail.example.com` — Cloudflare proxied
- `mail.example.com` — DNS-only (not proxied, as required for mail services)
-The issue
When issuing a Let's Encrypt certificate through CWP AutoSSL, the main domain and proxied SANs are validated successfully, but validation fails when including `mail.example.com`.
Depending on the operation, CWP displays one of these messages:
- `None of SAN it is pointed.`
- `At this moment your domain can not be validated please try again in some minutes.`
I reproduced the same behavior on another server.
-Investigation and findings
I confirmed that CWP uses HTTP-01 validation through the following ACME configuration:
Code Select
Le_Webroot='/usr/local/apache/autossl_tmp/'
Since `mail.example.com` is DNS-only, Let's Encrypt must connect directly to the server to complete HTTP-01 validation. However, the external firewall restricts inbound TCP/80 to Cloudflare IP ranges.
As a test, I temporarily allowed inbound TCP/80 from all IPv4 and IPv6 sources, then:
The certificate was immediately issued successfully, including all SANs.
After issuance, I removed the temporary firewall rule.
This is expected HTTP-01 behavior rather than a certificate issuance bug in CWP.
-Questions
1. Does CWP AutoSSL support DNS-01 validation using the Cloudflare API, including the main domain and all SANs?
2. If DNS-01 is not currently supported, is there any plan to implement it?
3. Is there an officially supported method to use certificates issued and renewed independently through `acme.sh` (DNS-01), while preserving CWP's certificate installation, mail services integration and automatic renewals?
4. Is there an officially recommended or supported solution for automatically issuing and renewing SSL certificates in this scenario, without requiring unrestricted inbound HTTP access?
Ideally, I would like to continue using CWP's built-in AutoSSL functionality. However, I'm also open to managing certificates through `acme.sh` with DNS-01 validation, provided they can be reliably installed and used by CWP and its associated services, including mail, without conflicts during future updates.
Temporarily opening TCP/80 works as a manual workaround, but I'm looking for a reliable, fully automated solution that can be applied consistently across multiple CWP servers.
Any guidance or recommendations would be greatly appreciated.
Thank you!
#26
Other / Re: Contact CWP Bug tracking s...
Last post by luca - November 14, 2026, 02:58:35 PMAll ok now, their support improved greatly now, theyre doing a great job.
#27
Information / Re: need to rename username fo...
Last post by luca - November 14, 2026, 02:57:56 PMSent to devs.
#28
Installation / Re: Upgrade from AL8.10
Last post by Wonder - November 14, 2026, 12:35:47 PMQuote from: stkontra on November 14, 2026, 09:40:13 AMI'm also wondering if it's possible to elevate from alma 8 to alma 10 without any compatibility issues in cwp pro?Just to add some more details to my previous post (now I can't edit my previous post):
My migration was performed from a server running AlmaLinux 8.10 with CWP Pro to a fresh installation of AlmaLinux 10 with CWP, using the built-in CWP-to-CWP migration tool. It was not an in-place OS upgrade.
The migration was successful, and I was particularly impressed by how much of the configuration was transferred automatically.
A few things I verified:
- DNS zones: The DNS zone was migrated automatically, including the existing records. CWP also replaced the old server's IPv4 addresses with the new server's IPv4, including the SPF record.
- IPv6: The original IPv6 addresses were preserved, so I updated them manually to match the new server.
- DKIM: The main domain's DKIM configuration and private key were migrated successfully. I verified that the private key was byte-for-byte identical on both servers using SHA256.
- DNS validation: After updating the IPv6 records and the SOA serial, the migrated zone passed `named-checkzone` validation and loaded successfully in BIND.
Overall, I'm very pleased with the improvements to the migration tool. The automatic DNS zone migration and IPv4 replacement were particularly nice surprises!
Of course, I'm still performing post-migration checks, so I wouldn't claim that every possible configuration has been fully verified yet.
Great work, CWP team!
#29
CentOS-WebPanel Bugs / Re: Mod Security
Last post by muscator - November 14, 2026, 12:30:47 PMQuote from: 6Sense on November 14, 2026, 03:06:06 AMI switched to latest rules via modsec UI (CWP 1.30.12) and it ran OWASP 3.x which is not desireable so I had to revert.
I think most of us now are all running OWASP 4.x using @starburst work around due to modsec rules being outdated for so long to remain secure.
I agree - therefore it also seems a little confusing, that in cwp->mod security it states "Latest - with automatic updates" when in fact both mod sec and the dataset is if not obsolete, then rather old
In the newest versions CWP states that all applications etc always - from now on - will contain newest versions of anything present as application in cwp
Owasp 3.x rules are indeed obsolete as per Q326:
CRS 3.3.0 July 1, 2020 6 years, 4 months old End-of-Life (Q3 2026)
So
I see in Edge 2.x that modsec at least is on newer version than earlier, but as you mention it seems as the rules still are version 3.x instead of 4.x
Hopefully this will be corrected soon in order to live up to the label stating that it uses 'latest version'
Funny to see that the Comodo version also states 'latest version' - this is not incorrect, as the last version was "1.240" in 2024....
 but maybe a false security to urge newbies to use the Comodo version with 'latest' rules from 2024 and that is not good for anyone....
Furthermore CWP writes that in the Edge version, modsec is updated to use 2.9.8, which is also obsolete and indeed not the latest version:
• Release Milestone. Version 2.9.8 was the first major maintenance update after the project was officially transferred from Trustwave to OWASP in 2024.
• Current Status. It is outdated and missing several critical security patches. Since September 2024, the OWASP ModSecurity team has released multiple patches to fix Denial of Service (DoS) and memory vulnerabilities, bringing the current v2 branch up to v2.9.15
#30
CentOS-WebPanel Bugs / Cant access error logs
Last post by anandmys - November 14, 2026, 11:35:24 AMUsing CWPpro version: 2.0.6 on AL8.10
User panel - >File managements - Log viewer
Dropdown doesn't show the domain name
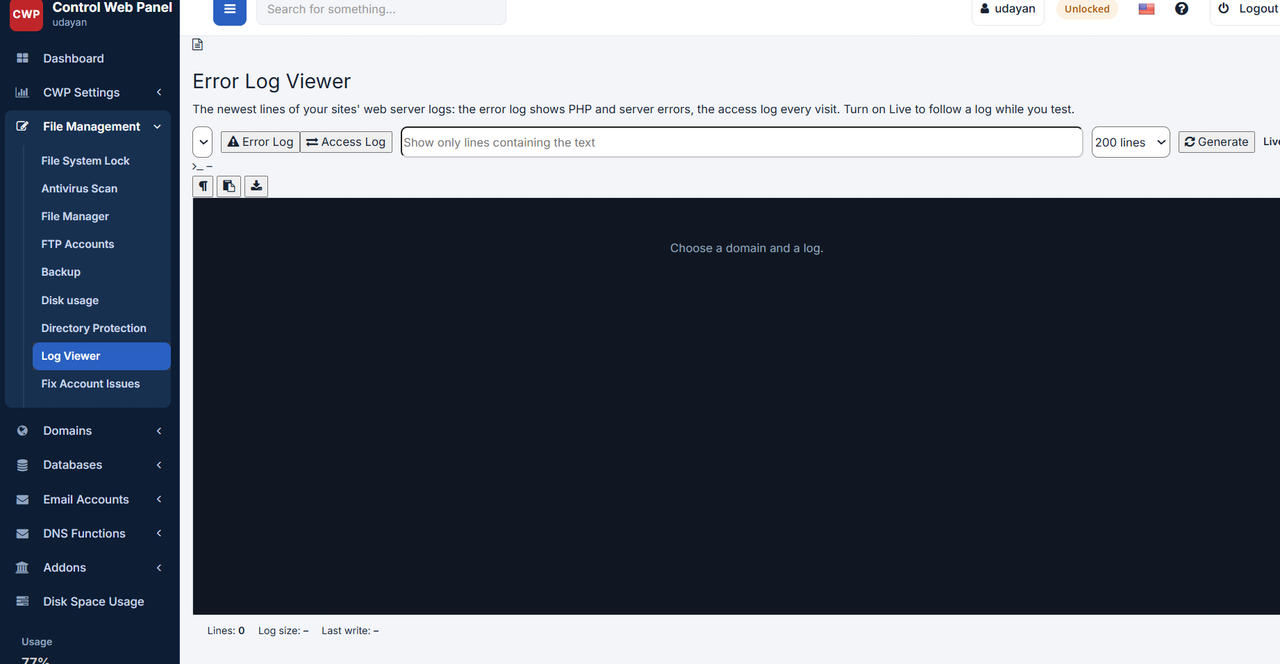
User panel - >File managements - Log viewer
Dropdown doesn't show the domain name